Zero-day defense
Block zero-day exploits and emerging threats with rules you don't need to update.
Global performance
Azion uses globally distributed infrastructure to keep your applications secure and fast.
Low false positives
Security rules that can automatically adapt to your application to stop only malicious traffic.
Distributed protection across every request
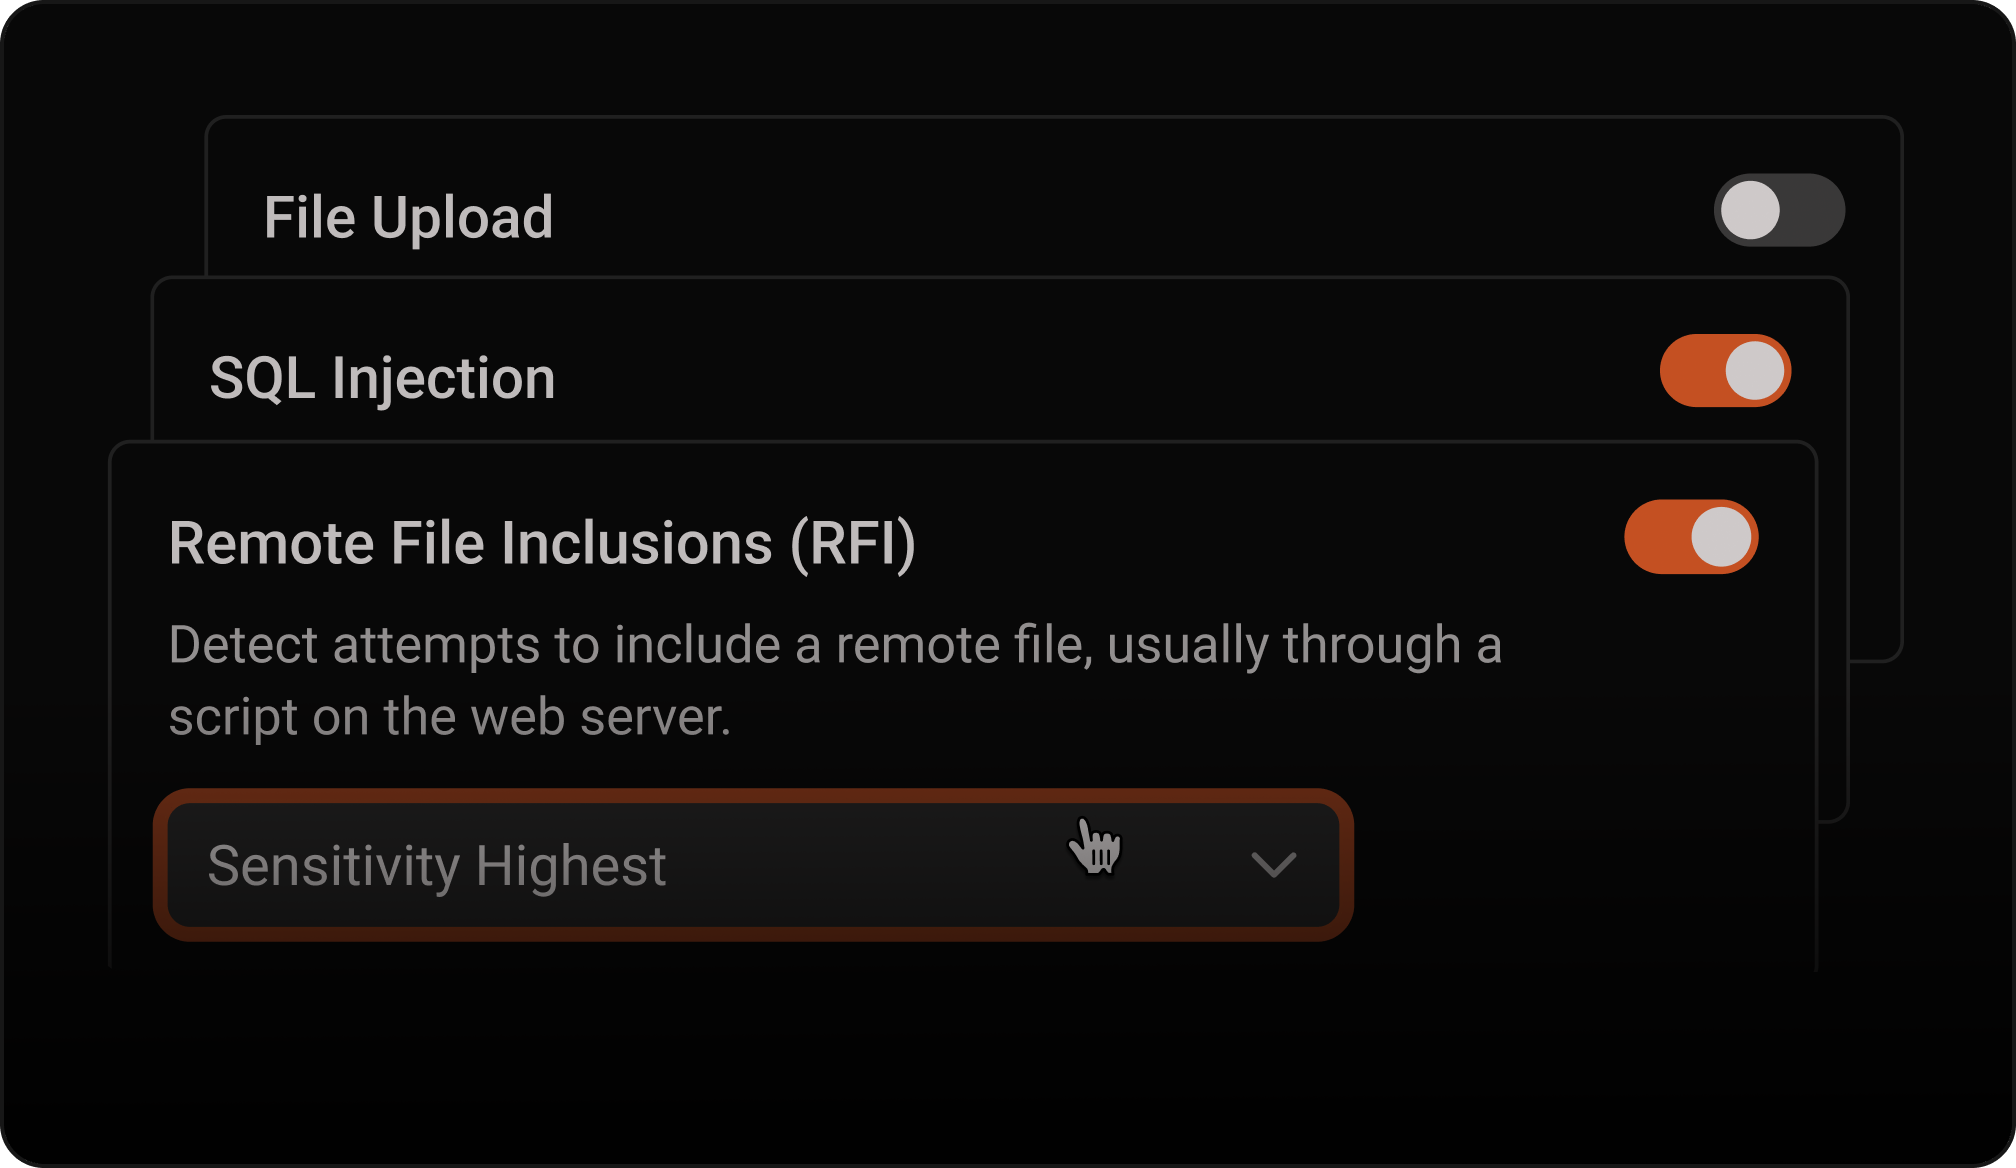
Enable OWASP protection with customizable rules
Enable preset OWASP protections and tune sensitivity to reduce false positives while keeping applications available. Run multiple WAF profiles per application to match different traffic patterns.
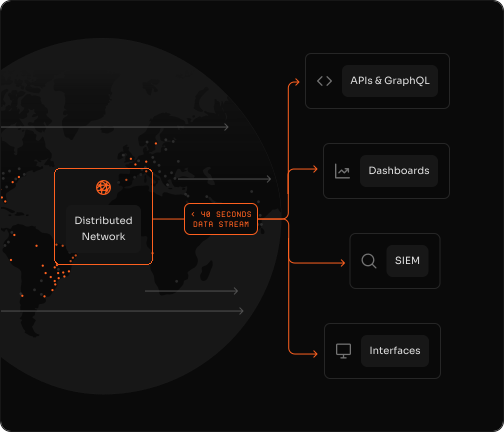
Stream security events for investigation and response
Send security events to SIEM, Splunk, Datadog, or analytics tools for fast visibility into suspicious traffic and application threats.
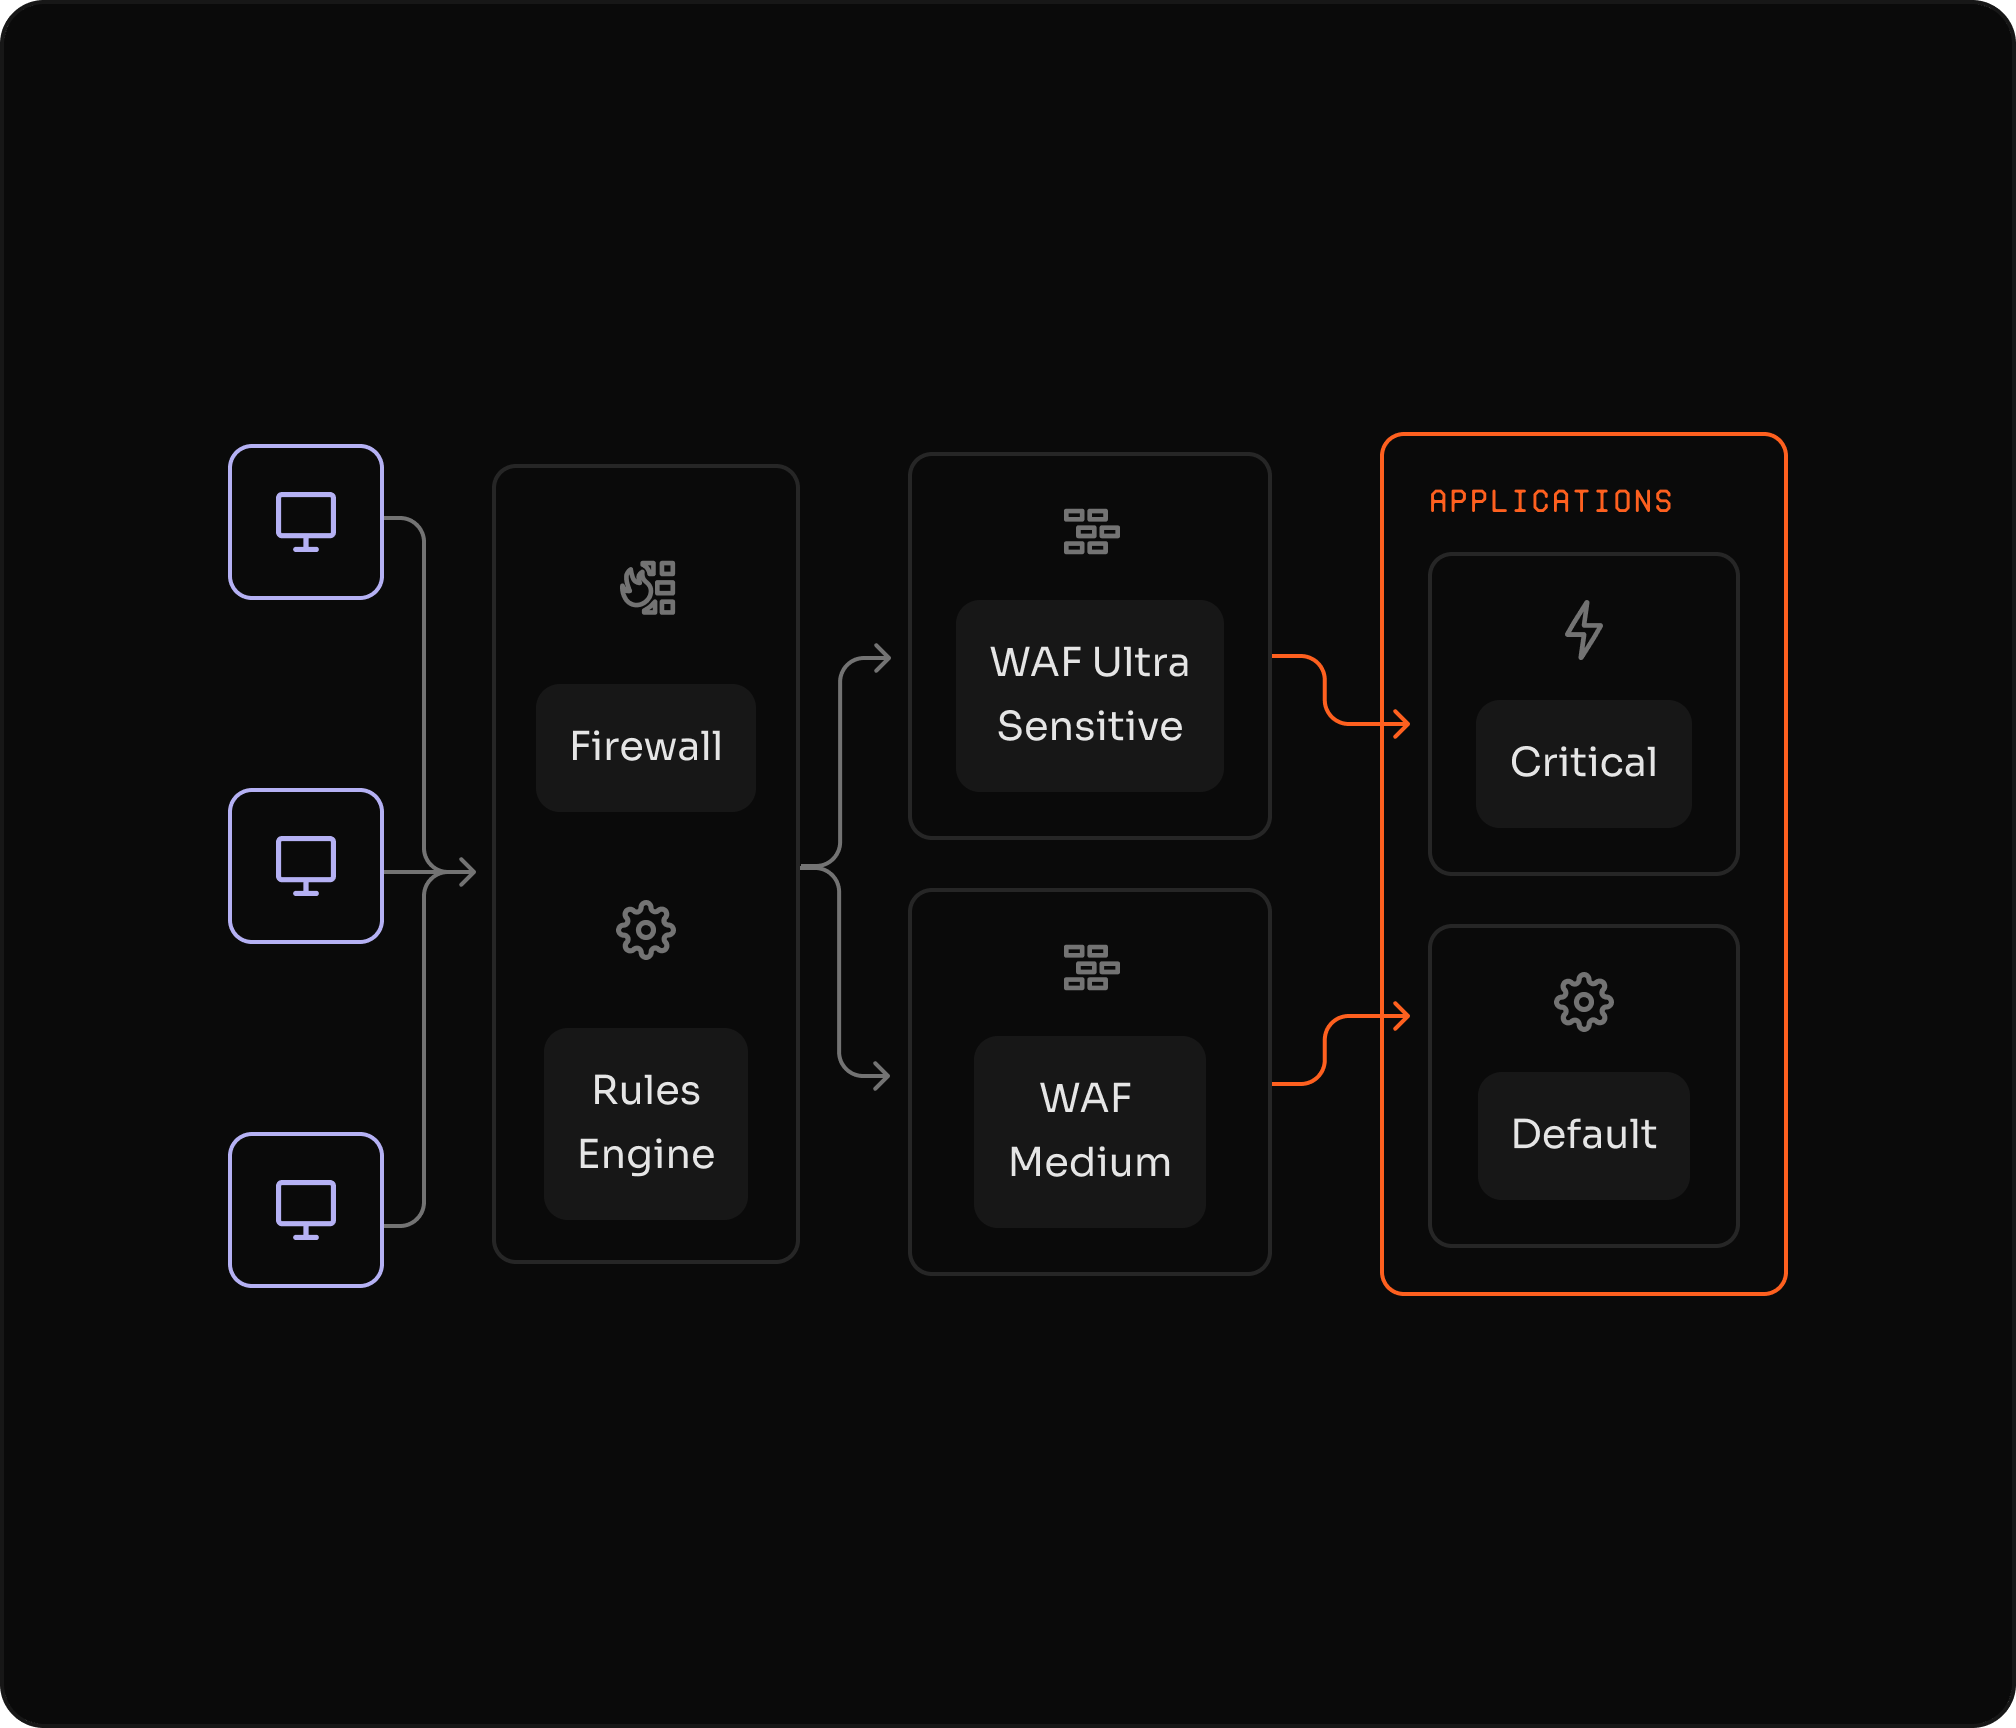
Detect advanced threats with behavioral analysis
Analyze requests with behavioral patterns and threat signatures to detect zero-day vulnerabilities and OWASP Top 10 attacks. Use Learning Mode to validate protections before enforcement.
Extend protection with custom logic
Write custom security rules with Functions to implement business-specific protections and automate mitigation workflows. Extend WAF behavior with your own detection logic or AI models.
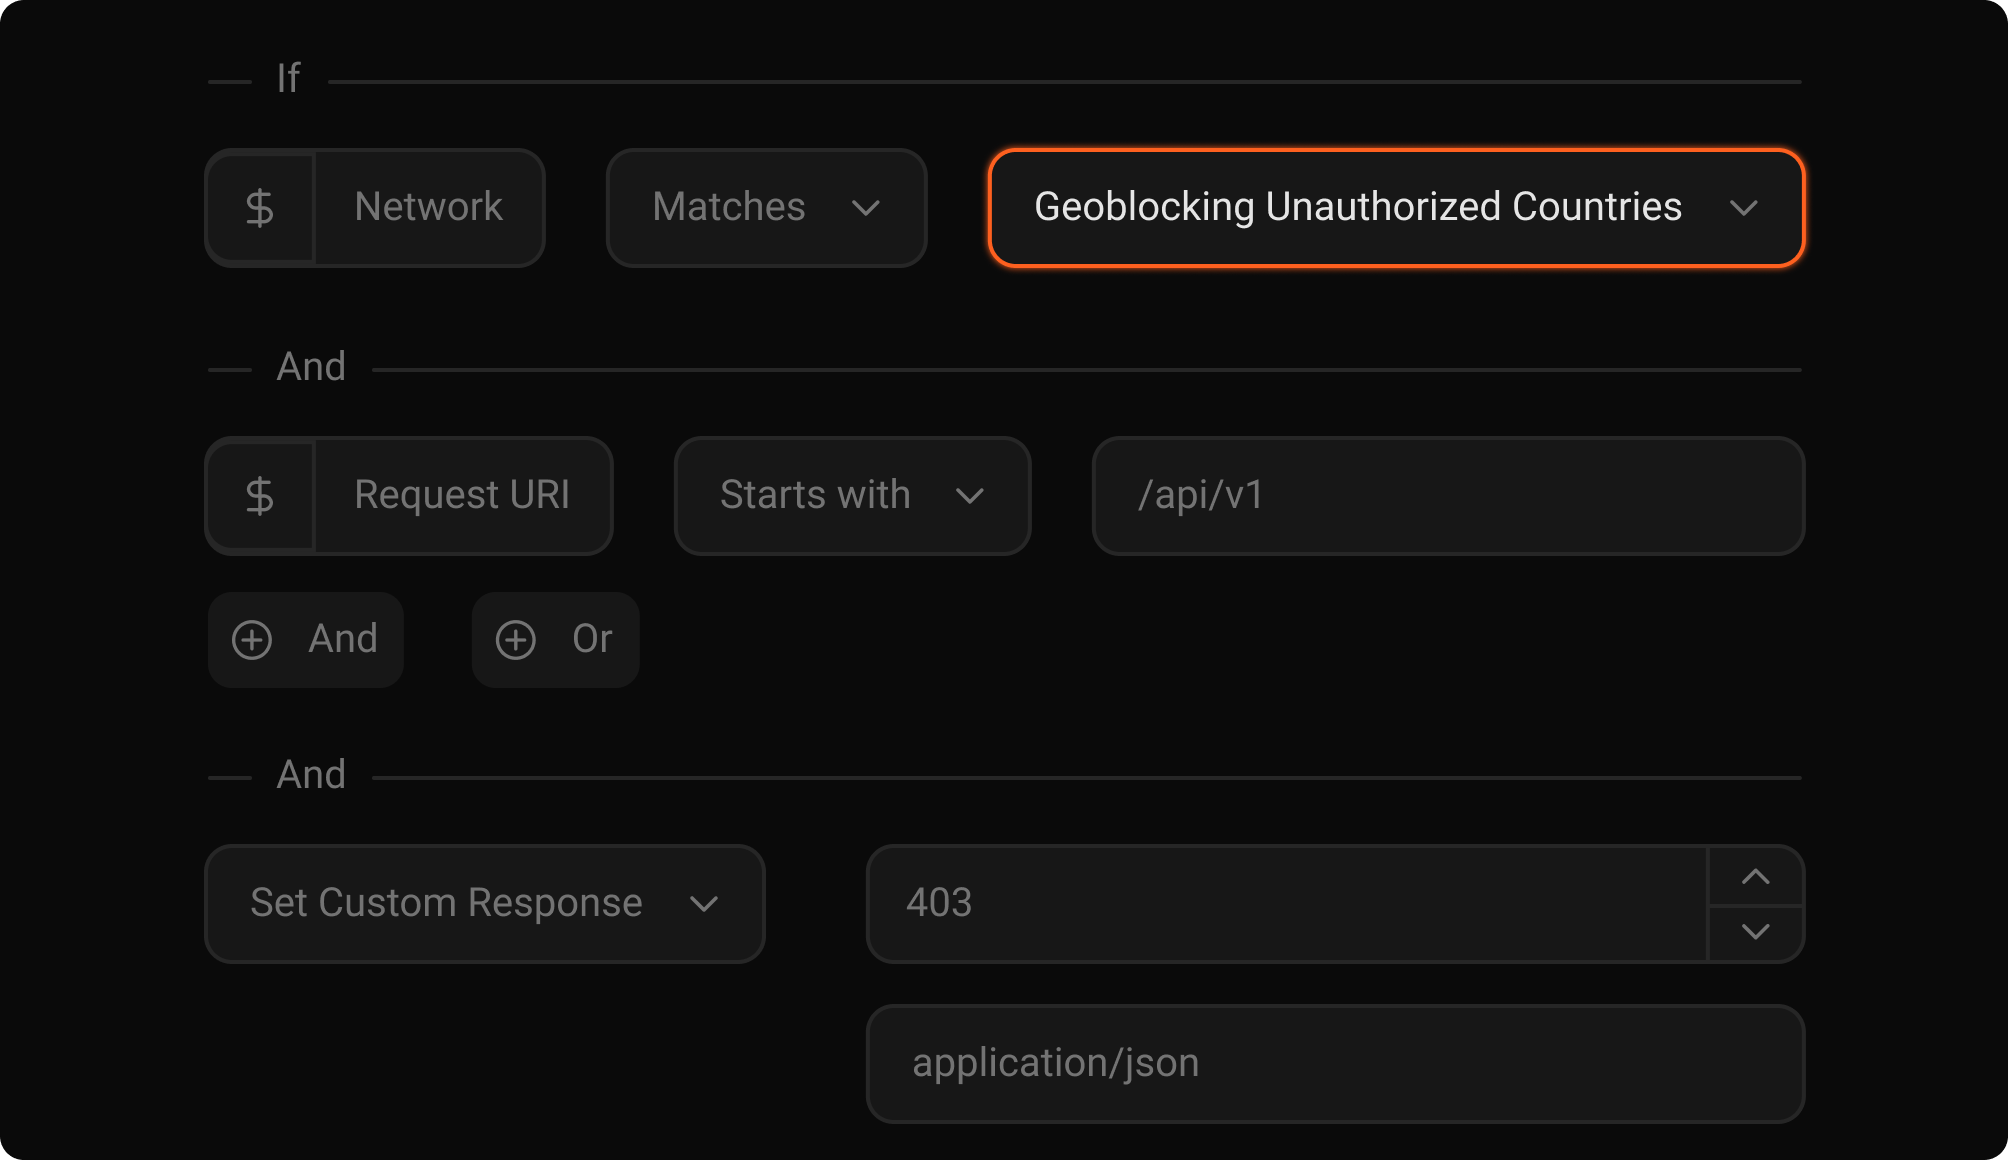
Adapt protection to legitimate traffic
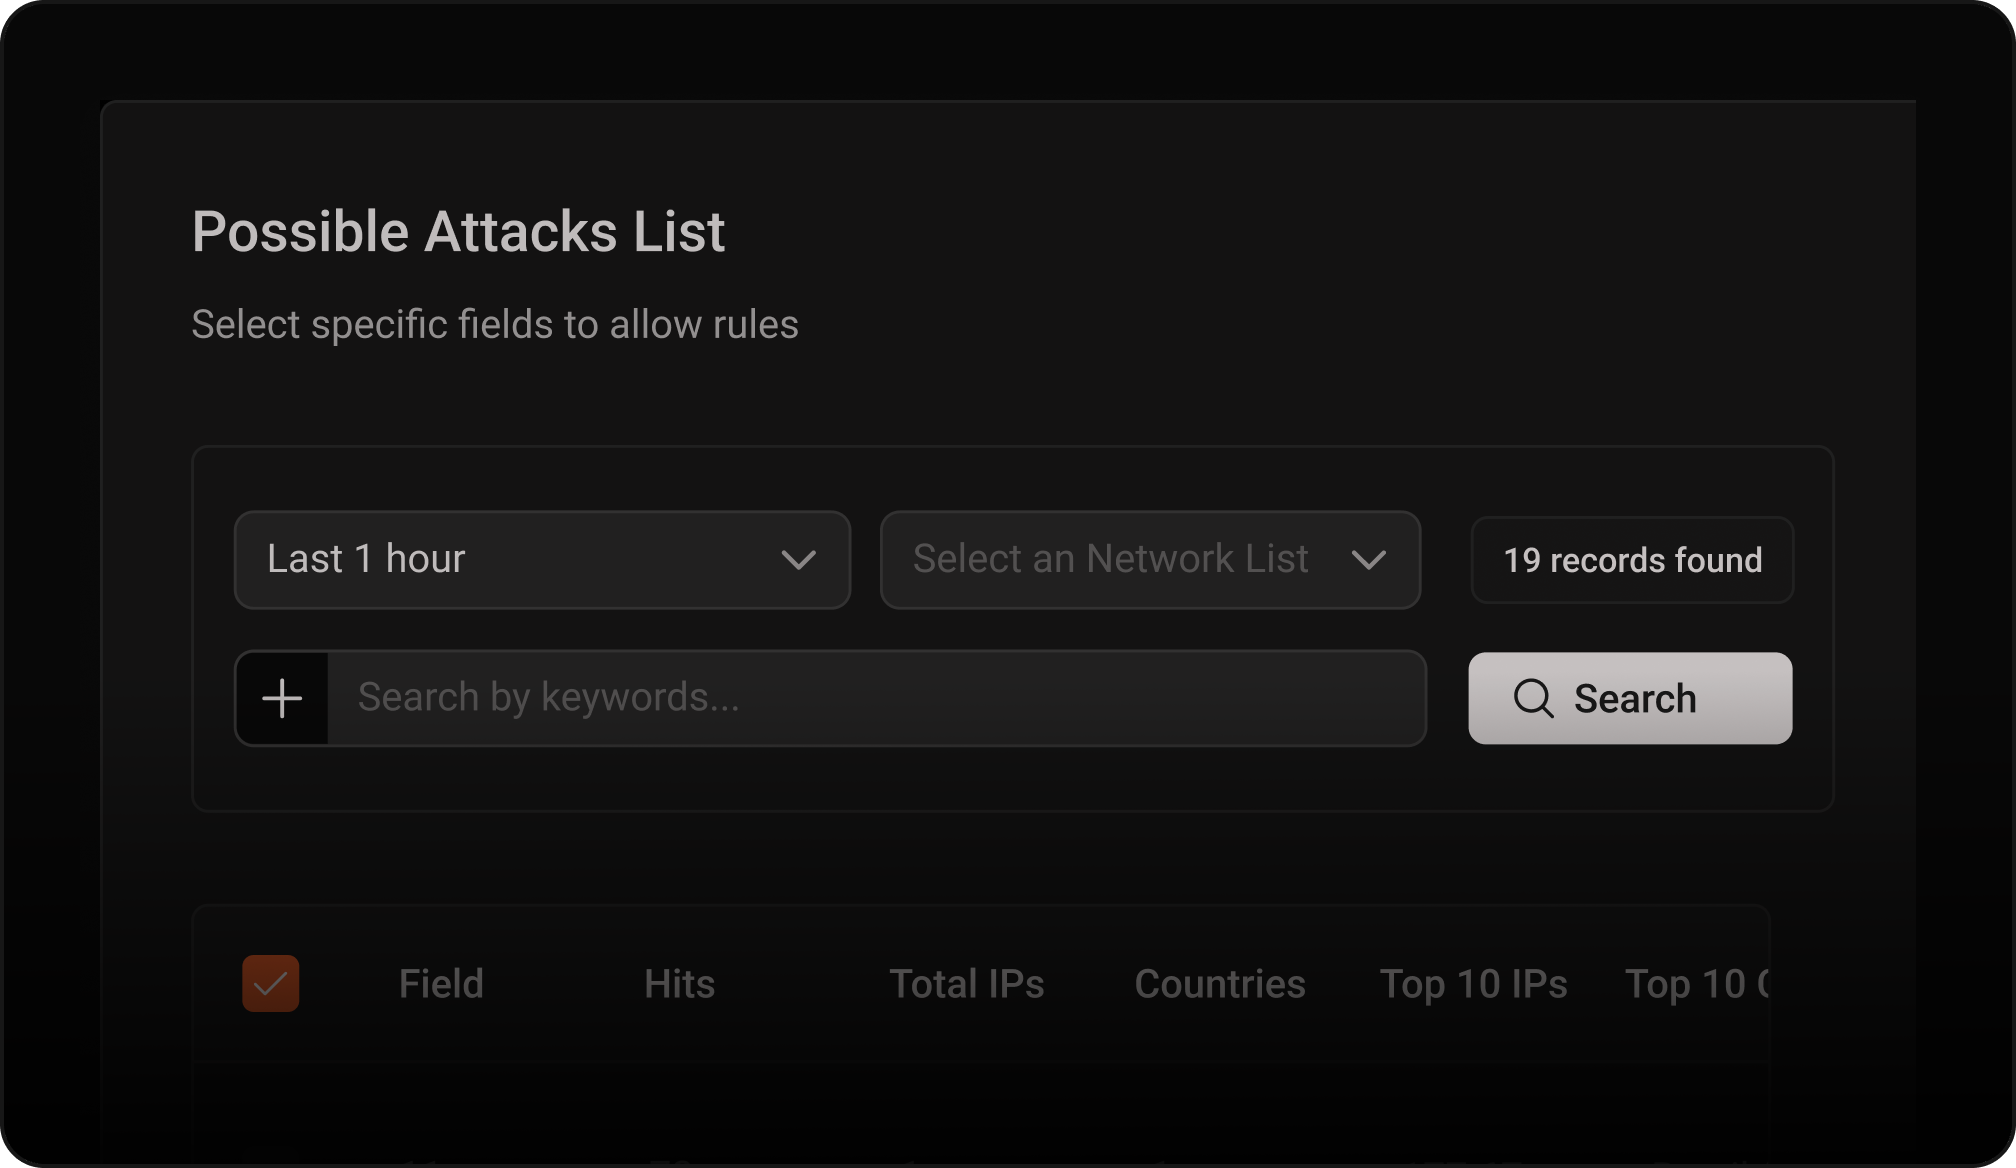
Create Custom Allowed Rules for trusted traffic patterns while blocking malicious requests before they reach your applications.


Azion shielded us from sophisticated cyberattacks and empowered us to modernize our infrastructure, reduce costs, and deliver the best shopping experiences to millions of customers.Protect critical applications and APIs
Frequently Asked Questions
Protected by default.Always on.
Get stronger protection, less attack exposure, and less operational overhead.