Block traffic before origin
Use Network Lists of IP addresses, CIDR blocks, ASNs, and countries combined with Rules Engine to create layered defense policies.
Eliminate bandwidth waste from attacks
Block abusive traffic on the Azion Web Platform so your origin servers never process malicious requests.
Propagate rules in seconds
Update Network Lists via Console or API and see changes live across all locations in seconds. No service interruptions, no downtime windows.
Protect any environment consistently
One set of rules protects workloads across AWS, GCP, Azure, on-premises data centers, and hybrid architectures. Consistent protection regardless of where your applications are hosted.
Share lists across firewalls
Create a catalog of Network Lists and reference them across multiple Firewall configurations. Update once, propagate everywhere.
Automate threat response at scale
Stream security events to your SIEM and trigger automated playbooks to update Network Lists via API. Use Functions to implement programmable, per-request decisions.


Azion shielded us from sophisticated cyberattacks and empowered us to modernize our infrastructure, reduce costs, and deliver the best shopping experiences to millions of customers.Block threats at the network layer, before they consume resources
Programmable network-layer security
Define access policies with lists that combine IP addresses, CIDR blocks, geolocation, ASNs, and reputation scores. Reference these lists directly in the Firewall Rules Engine. Updates propagate automatically across all associated firewalls, with no service interruption.
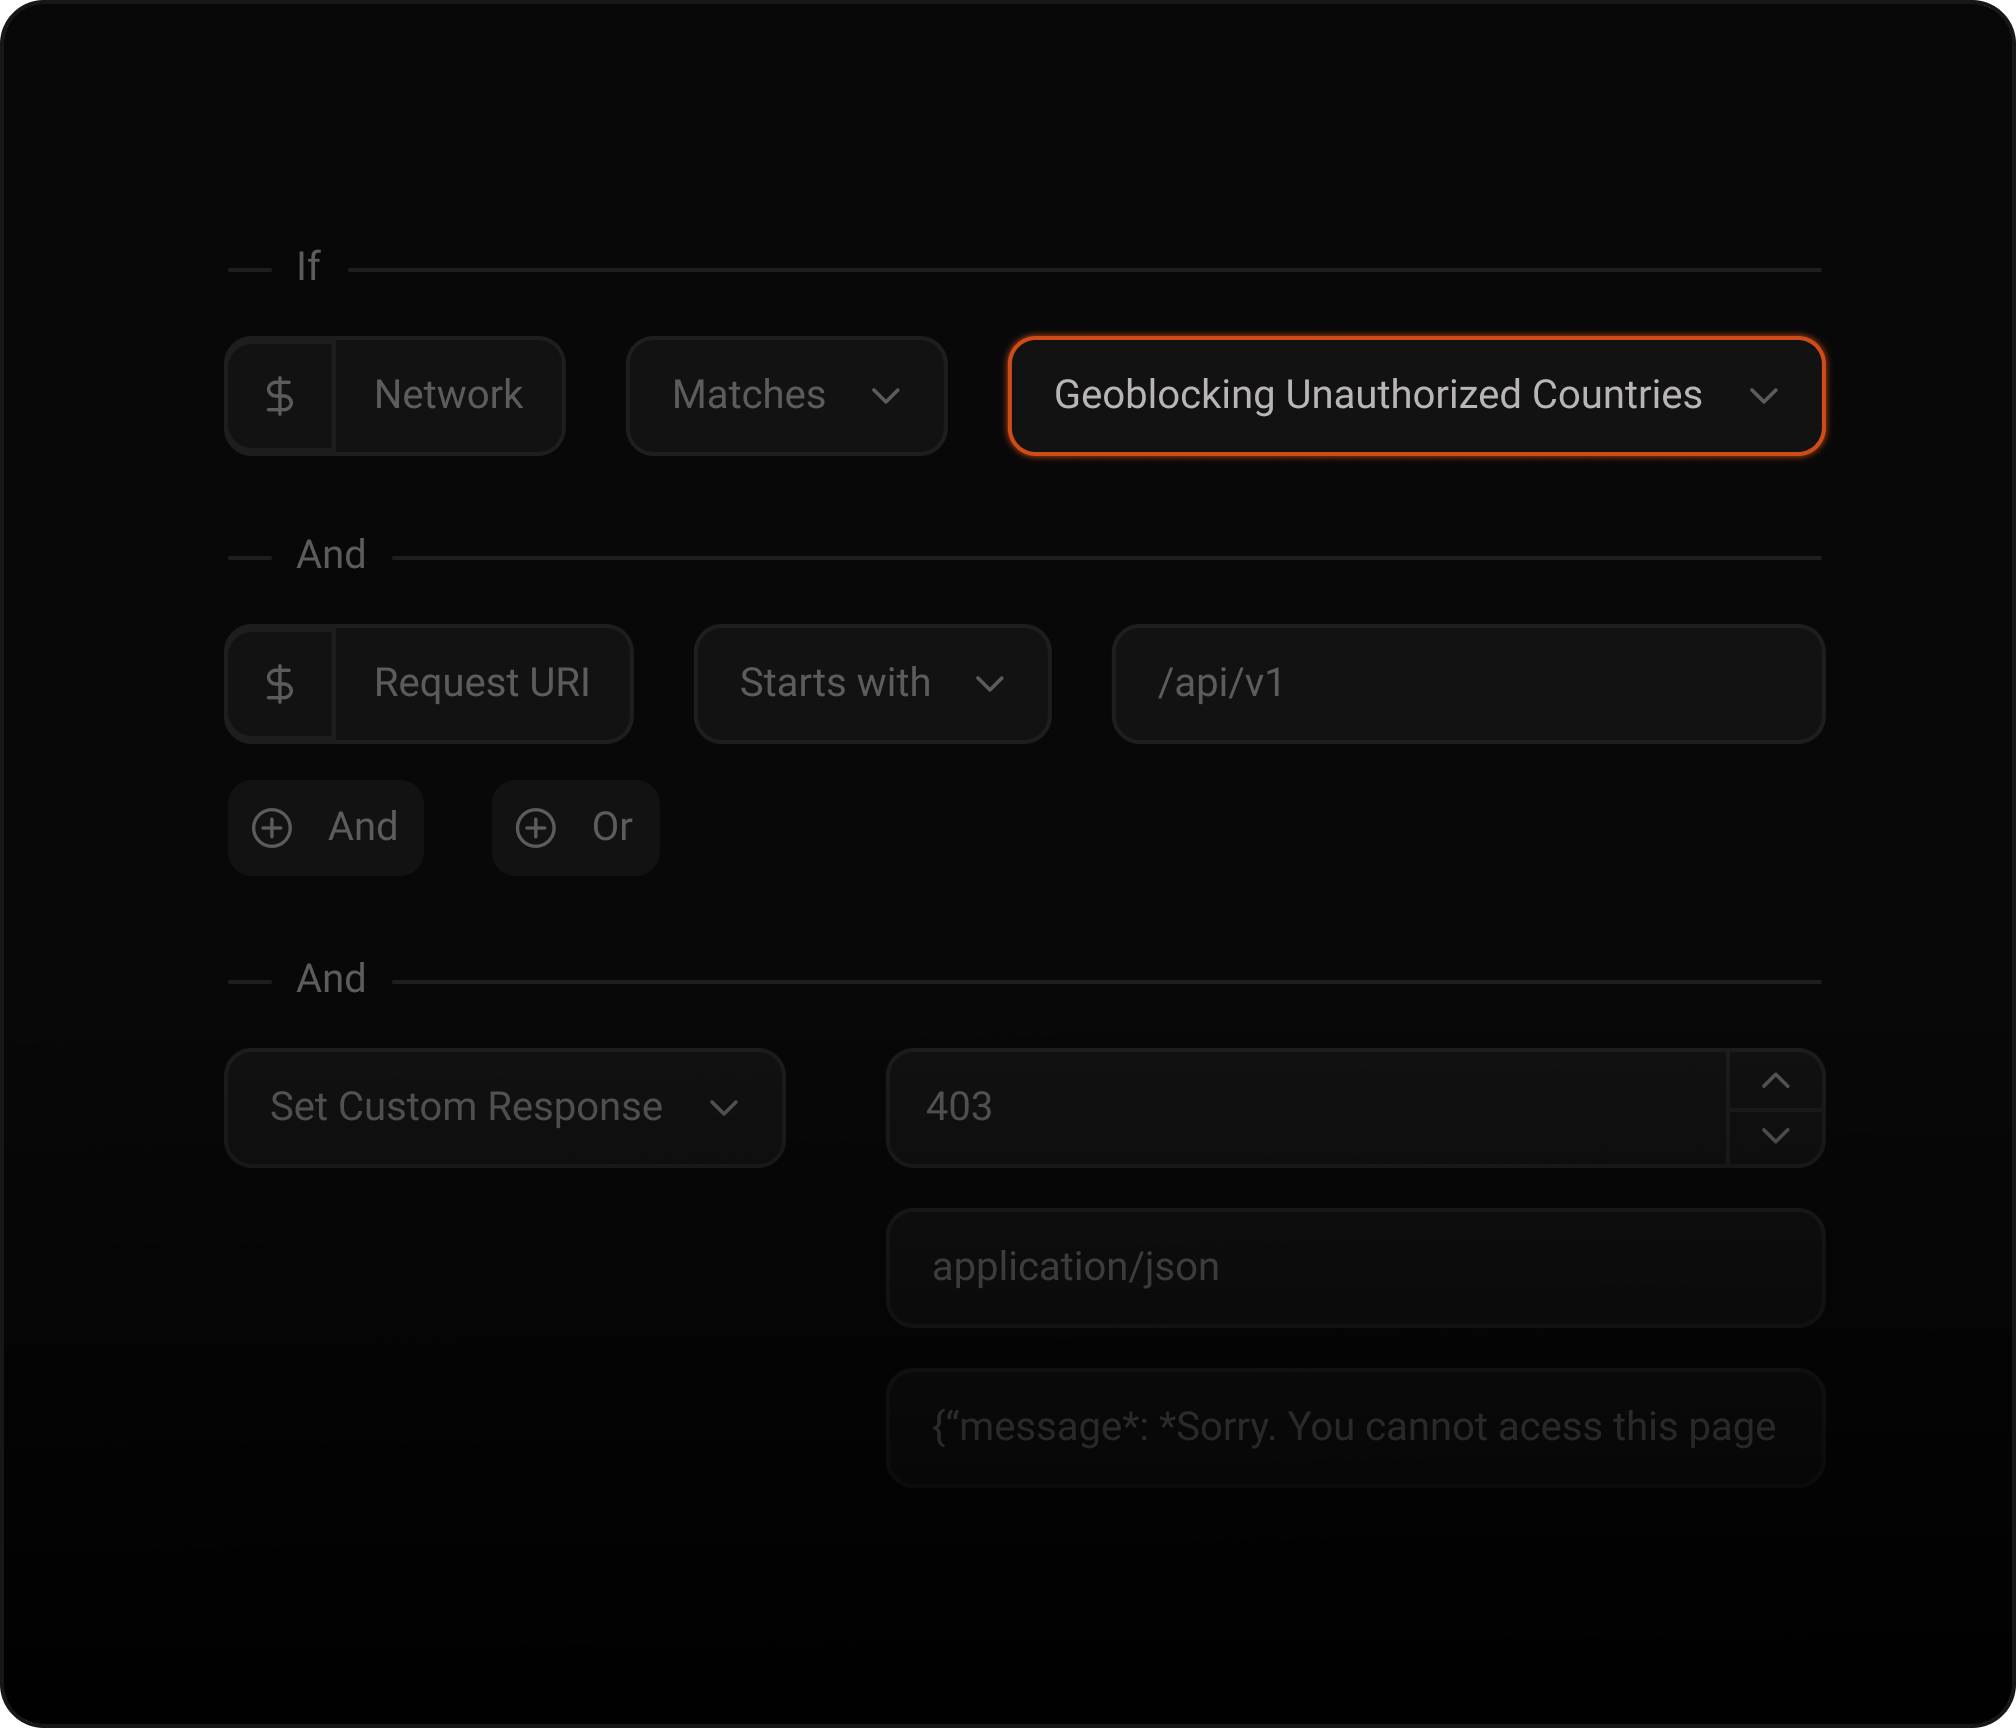
Rule-based traffic control with centralized list management
Create custom allowlists and blocklists using IPs, CIDR blocks, ASNs, countries, or Azion-managed lists like Tor Exit Nodes. Segment access by region or network type, and share the same lists across multiple firewalls for consistent policies at scale.
Automated threat response with real-time event streaming
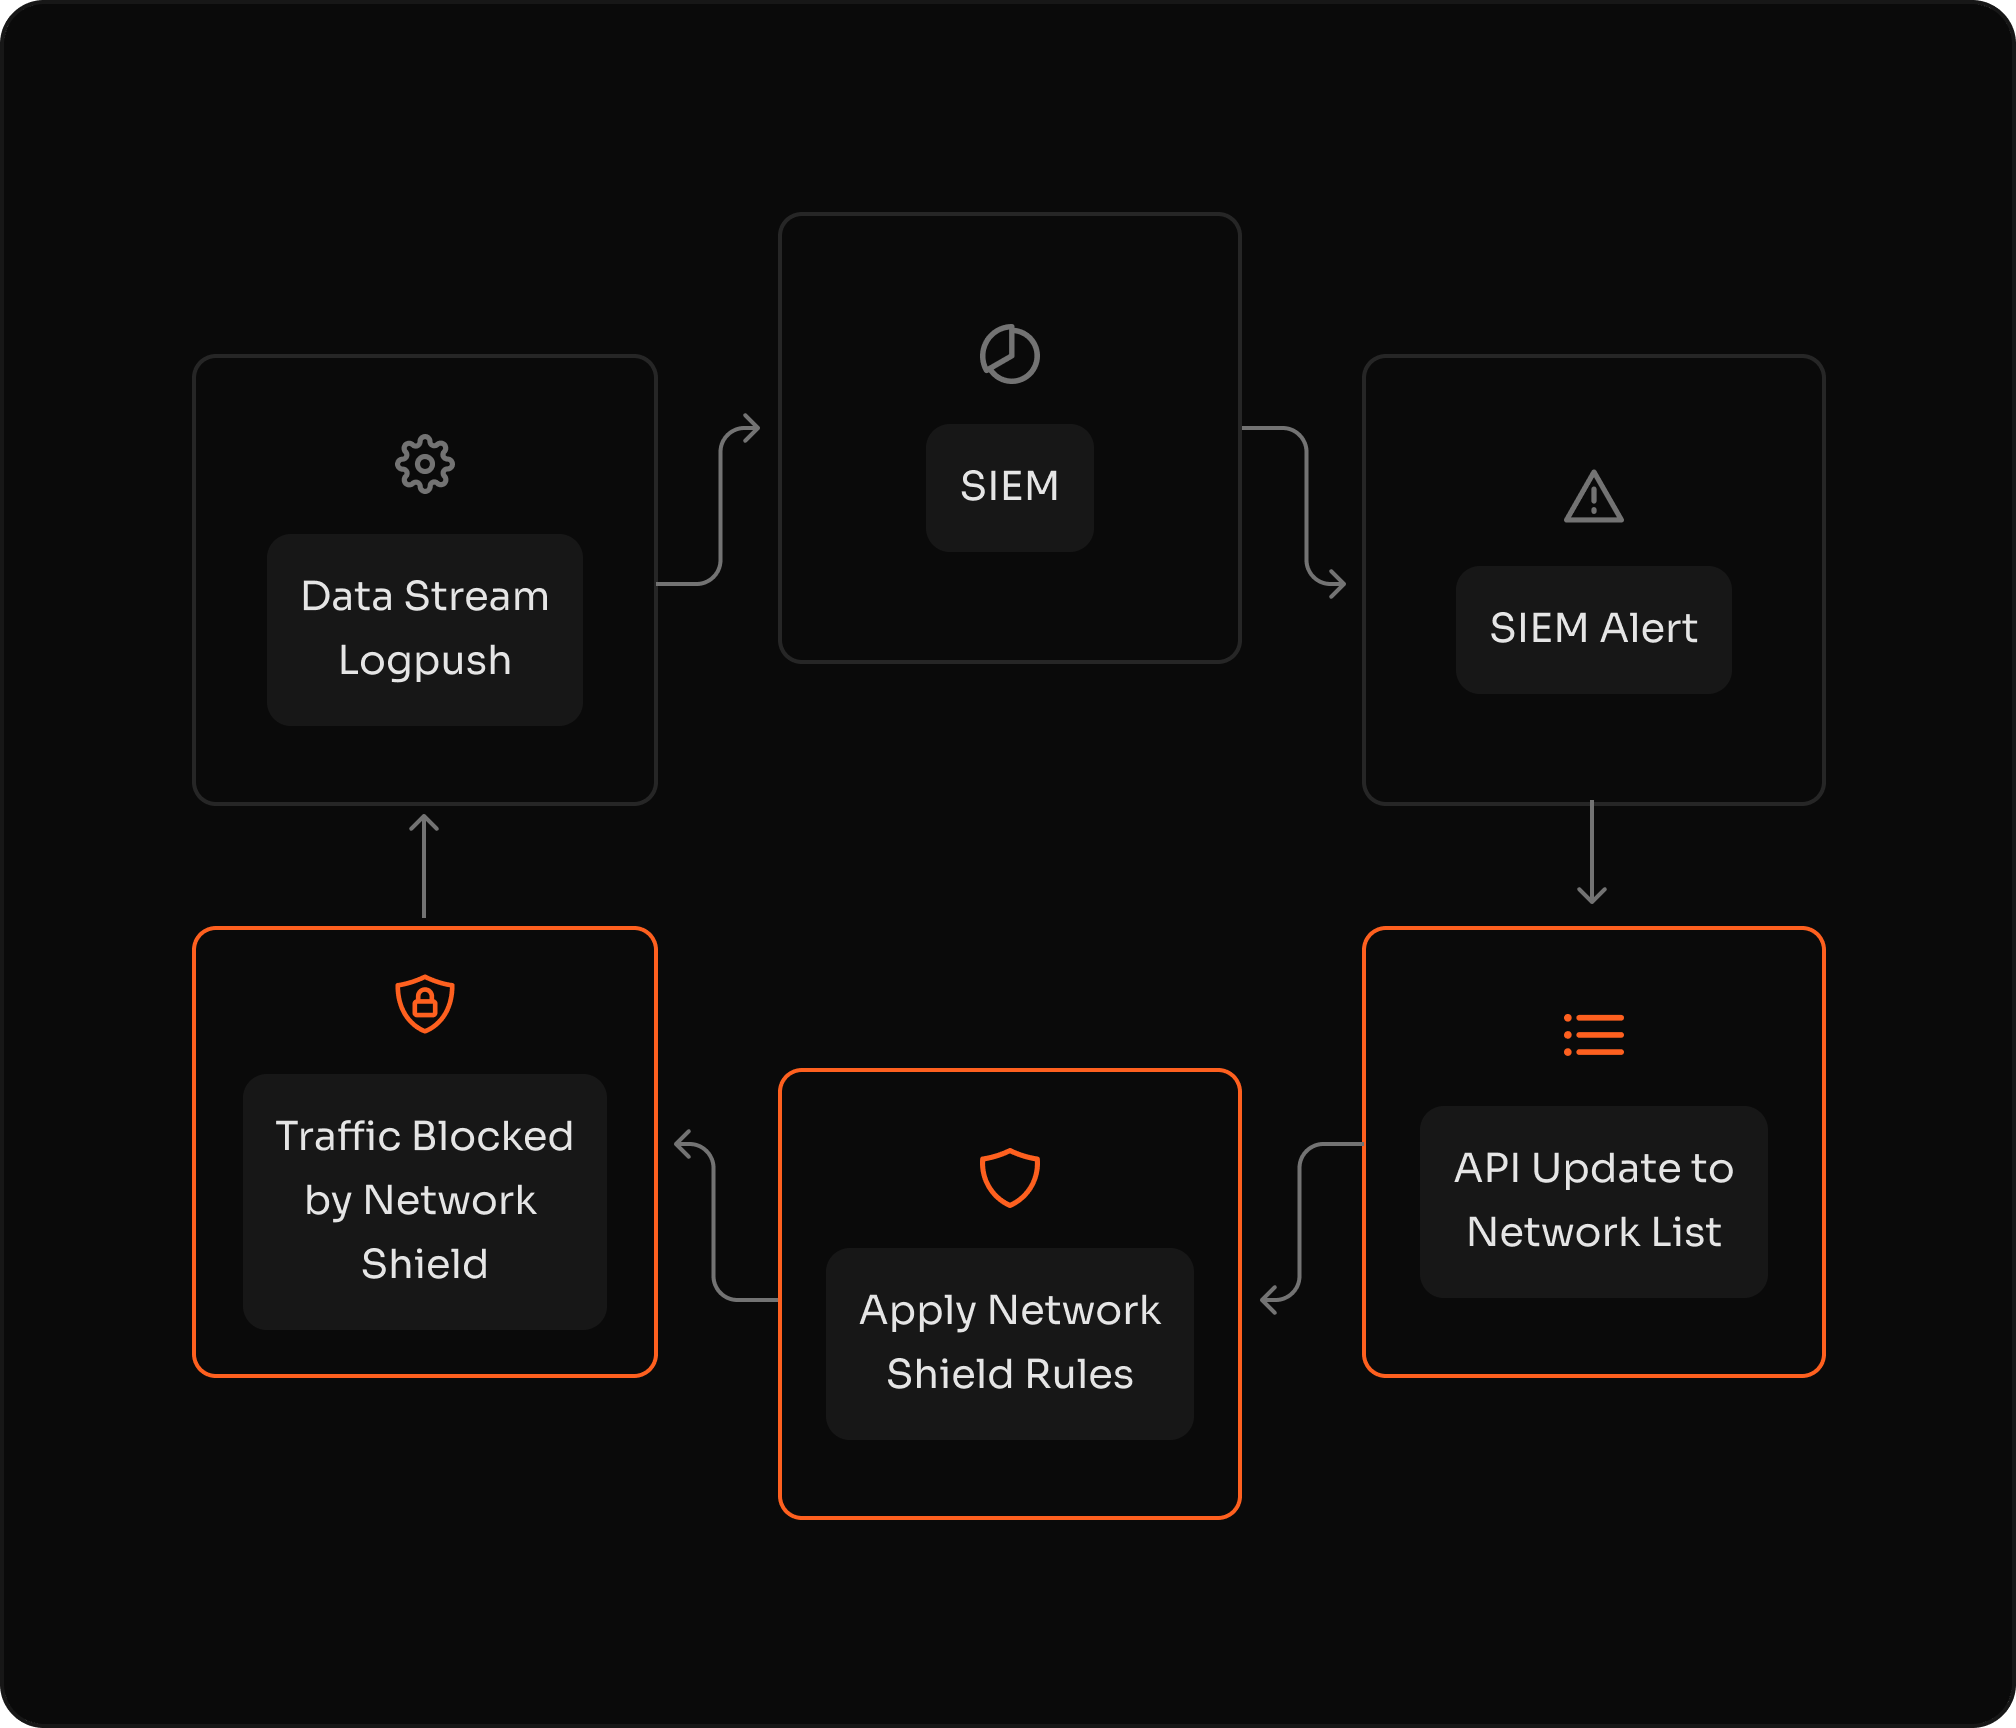
Stream events to your SIEM in real time and trigger automated playbooks to update Network Lists via API. Changes propagate in seconds. Use Functions to implement programmable, per-request blocks and adapt your risk response dynamically.
Lock down your infrastructure
Use Origin Shield to restrict inbound traffic to your origin servers exclusively from Azion's trusted IP addresses. The dynamic Network List is maintained by Azion and updated automatically. Configure your origin's firewall to accept only Origin Shield addresses, establishing a Layer 3/4 perimeter that blocks all direct external access.
Frequently Asked Questions
Protected by default.Always on.
Get stronger protection, less attack exposure, and less operational overhead.